This is the second article in the ACX7k Metro Validation Series.
In this article, we validate the EVPN-VPWS feature and its scale on ACX7100-32C with 22.2R1 Junos-EVO image.
RFC-8214 describes the VPWS support with EVPN. EVPN-VPWS is a point-to-point ethernet service based on BGP MPLS connecting Customer Edge Devices (CEs) across a Provider Edge (PE) Network. The PEs of the network are connected over MPLS technology signalled via LDP, RSVP or SR-MPLS.
JUNOS supports EVPN-VPWS functionality with the "evpn-vpws" Instance Type.
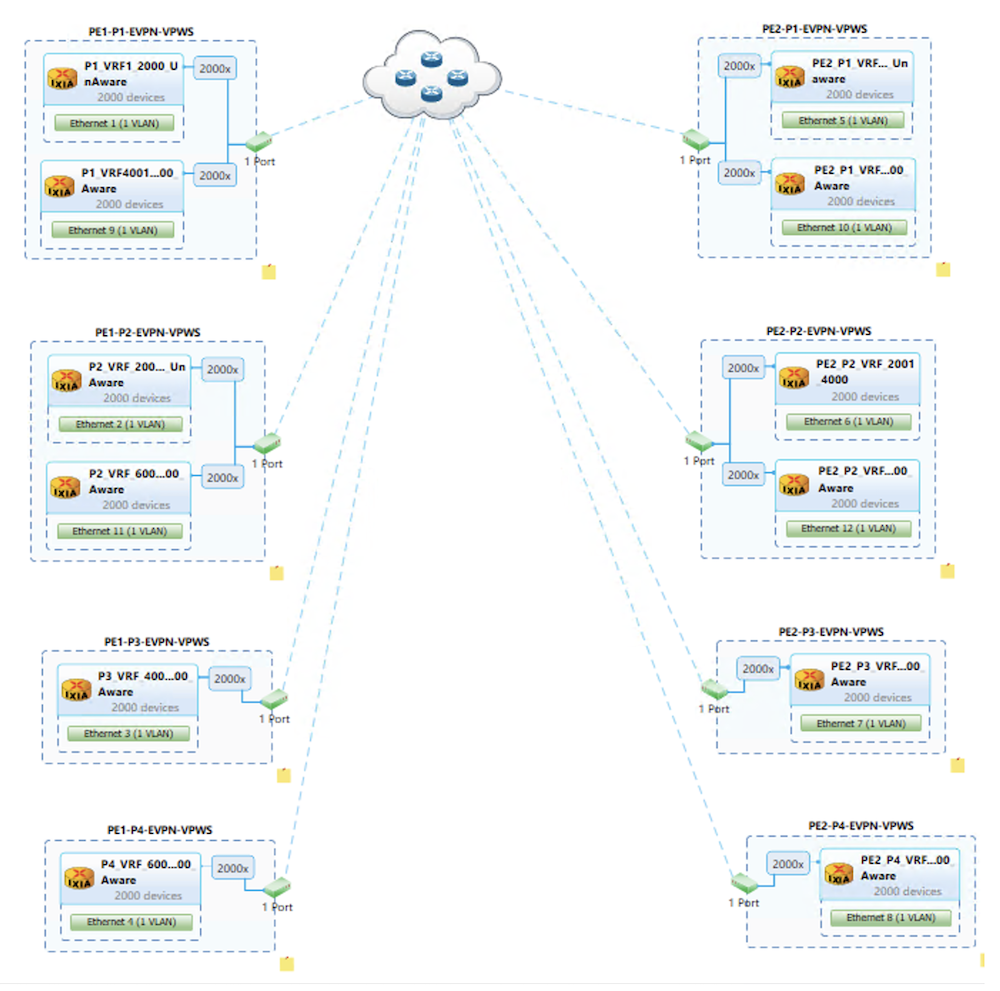
In this test, we create 8,000 EVPN VPWS Instances on ACX7100-32C:
But the ACX7024 Scale is not covered in this article (same features but different scale are expected on this platform).
Please note that despite sharing the same ACX moniker, the ACX7000 products are different products than ACX500/710/1000/1100/2100/2200/4000/5000/5400/6000. They are powered by different Packet Forwarding Engines (PFE), and support different feature sets and scales.
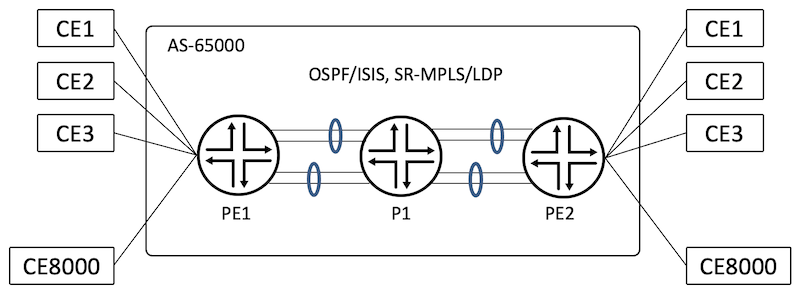
CEs are simulated using a traffic generator. PEs are connected to CEs using 4x 100G links and to the core using 8x 100G links, which are bundled in 2x LAGs each having four links.
The ACX7100-32C is the Device Under Test (DUT). The underlay transport used for testing is SR-MPLS with both OSPF and ISIS protocols individually. In this validation, we also covered LDP as the underlay transport. The CE-bound interface configurations are of SP-Style (see glossary).
The first step to verify the EVPN-VPWS service is to make sure that the PE devices are having BGP established with evpn-signalling. As shown below from PE1, BGP is in "established" state for the Peer PE2 (12.1.1.3) and bgp.evpn.0 table got populated with Type-1 Infra routes.
regress@PE1> show evpn vpws-instance METRO_EVPN_VPWS_1
Instance: METRO_EVPN_VPWS_1, Instance type: EVPN VPWS FXC
  Route Distinguisher: 12.1.1.1:1
  Number of local interfaces: 1 (1 up)

    Interface name  ESI                            Mode          Role       Status     Control-Word    Flow-Label-Tx    Flow-Label-Rx
    et-0/0/0.1      00:00:00:00:00:00:00:00:00:00single-homed    Primary    Up         No              No               No
        Local SID: 1001 Advertised Label: 16
        Remote SID: 2001
            PE addr         ESI                           Label  Mode           Role     TS                      Status
            12.1.1.3        00:00:00:00:00:00:00:00:00:00 16     single-homed   Primary  2022-10-21 02:40:19.916 Resolved
  Number of protect interfaces: 0

regress@PE1>
The routes of METRO_MAC_VRF_1 instance are shown below.
regress@PE1> show evpn vpws-instance METRO_EVPN_VPWS_4001
Instance: METRO_EVPN_VPWS_4001, Instance type: EVPN VPWS FXC VLAN AWARE
  Route Distinguisher: 12.1.1.1:4001
  Number of local interfaces: 2 (2 up)

    Interface name  ESI                            Mode          Role       Status     Control-Word    Flow-Label-Tx    Flow-Label-Rx
    et-0/0/0.2001   00:00:00:00:00:00:00:00:00:00single-homed    Primary    Up         No              No               No
        Local SID: 1002 Advertised Label: 4016
        Remote SID: 2002
            PE addr         ESI                           Label  Mode           Role     TS                      Status
            12.1.1.3        00:00:00:00:00:00:00:00:00:00 4016   single-homed   Primary  2022-10-21 02:40:23.424 Resolved

    Interface name  ESI                            Mode          Role       Status     Control-Word    Flow-Label-Tx    Flow-Label-Rx
    et-0/0/2.1      00:00:00:00:00:00:00:00:00:00single-homed    Primary    Up         No              No               No
        Local SID: 1001 Advertised Label: 4016
        Remote SID: 2001
            PE addr         ESI                           Label  Mode           Role     TS                      Status
            12.1.1.3        00:00:00:00:00:00:00:00:00:00 4016   single-homed   Primary  2022-10-21 02:40:23.424 Resolved
  Number of protect interfaces: 0

regress@PE1>
The BGP route table of the instance includes routes belonging to VLANs of the aware instance.
---
# This file contains the parameters for evpn vpws configuration building
# File Name: evpn_params.yaml
# Version: 1.0

#Host Name
host: 'PE1.englab.juniper.net'

#UserName and Password
username: 'regress'
password: 'xxxxx'

#Config Group Name
group_name: 'METRO_EVPN_VPWS'

#vrfname creation
vrf_id: 1

#maximum evpn instances
vrf_max: 10

#interface name
ifd_name: 'et-0/0/0'

#ifl_start unit
ifl_start_unit: 1

#vlan_id start
vlan_id_start: 1

#My AS no
local_as_no: 65000

#My Router ID
router_id: '12.1.1.1'

#EVPN Service Type:
enable_fxc: True
vlan_unaware_service: False
vlan_aware_service: True

#VPWS Service ID
vpws_local_service_id: 1001  # At PE1
vpws_remote_service_id: 2001 # At PE1
# vpws_local_service_id: 2001  # At PE2
# vpws_remote_service_id: 1001 # At PE2

# vpws_local_service_id: 1002  # At PE1 for vlanaware ifl-2
# vpws_remote_service_id: 2002 # At PE1 for vlanaware ifl-2
# vpws_local_service_id: 2002  # At PE2 for vlanaware ifl-2
# vpws_remote_service_id: 1002 # At PE2 for vlanaware ifl-2
In this article, we demonstrate the ACX7k (ACX7100-32C, ACX7100-48L, ACX7509) platforms scale for EVPN VPWS use-cases, proving these routers are ready for the Metro deployments and capable of delivering various ethernet business services of Metro. Next TechPost article will be dedicated to L3VPN scale validation.